Build Autonomous AI Agents That Work Safely
Learn how autonomous AI agents reason, act, and handle real business tasks.
What Are Autonomous AI Agents?
Autonomous AI agents are systems that pursue goals with limited human input. They can reason, plan, and execute multi-step tasks. They also react when new facts change the path ahead.
So, what is an autonomous AI agent in simple terms? It is software that can choose actions, use tools, and check results. A chatbot often waits for each prompt. An agent can keep working toward a goal after the first request.
For example, a support agent could find a customer record, check an order, draft a reply, and route an issue. It may ask a person to approve a refund. It does not need a person to direct every small step.
- Goal: The outcome the agent must reach.
- State: The facts and progress it holds during work.
- Actions: The tools it can call or tasks it can run.
- Checks: Rules that limit risk and catch errors.
This goal-directed behavior sets agents apart from basic scripts. A script follows fixed steps. An agent can pick a different path when a tool fails or data changes.
The Core Parts That Make an Agent Work
Most autonomous agents have six key parts. Each part has a clear job. Together, they form a loop that turns a goal into tested actions.
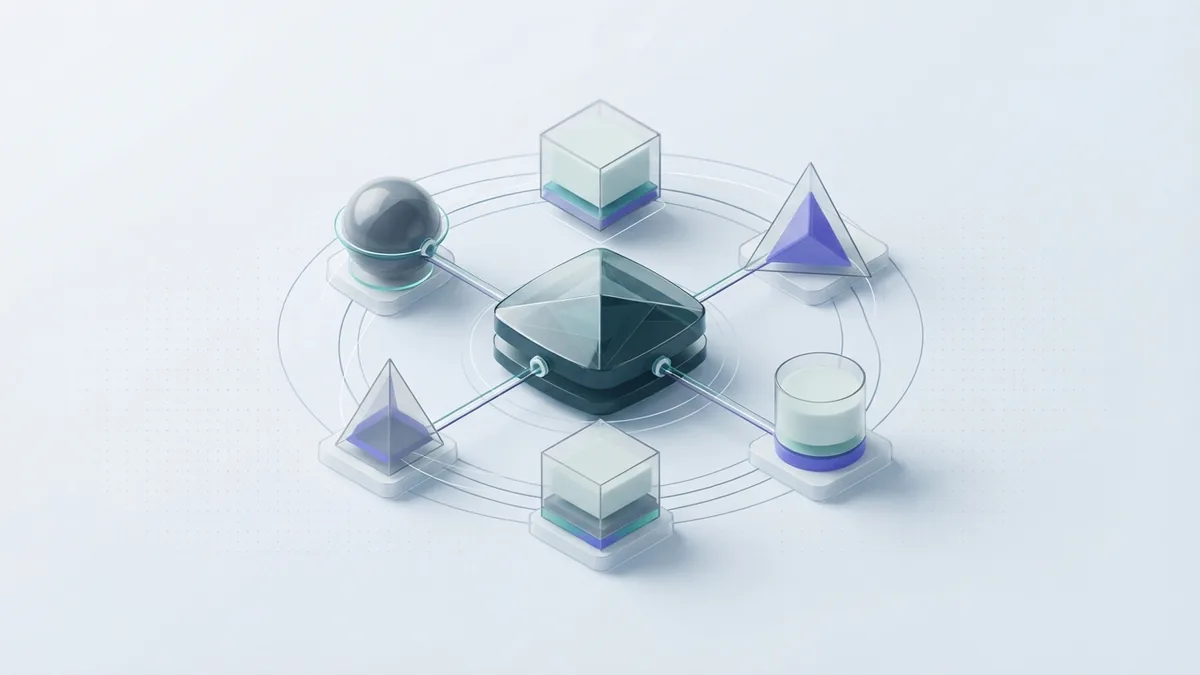
The reasoning model reads context and suggests the next step. The agent core manages the loop. It tracks the goal, current state, tool results, and stop rules.
The harness connects the core to tools and data. It sets tool formats, time limits, retries, and approval gates. A secure runtime runs code in a limited space. It blocks unsafe access to files, networks, and secrets.
Memory helps the agent keep useful facts. Short-term memory holds the current task. Long-term memory stores approved facts across sessions. Planning modules break large goals into smaller actions and revise them when needed.
| Component | Main role | Useful control |
|---|---|---|
| Reasoning model | Suggests plans and actions | Schema checks |
| Agent core | Runs the task loop | Step and cost limits |
| Harness | Connects tools and data | Allow lists |
| Secure runtime | Runs code with limits | Sandboxing |
| Memory | Keeps task context | Access and delete rules |
| Planning module | Breaks goals into steps | Human approval gates |
How Autonomous Agents Differ From Automation
Traditional automation follows a known path. It works well when inputs and outcomes stay stable. A rule may say, “If an order is late, send an email.”
An autonomous agent starts with an outcome. It then chooses a path based on the facts it finds. It can compare options, call several tools, and adapt when a step fails. That makes it useful for complex workflows with many possible paths.
Agents also support adaptive decision-making. A sales agent might find a lead, check account data, research recent activity, and draft a tailored plan. It can stop when data is missing. It can also seek approval before changing a record.
Autonomy still needs limits. A good system has narrow tools, clear goals, and a known stop point. More freedom does not always create better results.
Types of Autonomous AI Agents
There is no single agent design. Teams choose a type based on task length, risk, and data needs. Many products use more than one type at once.
- Reactive agents respond to events with little stored context. They suit alerts, routing, and simple support flows.
- Planning agents break a goal into steps before they act. They suit research, reporting, and process work.
- Tool-using agents call search, database, code, or business tools. They suit tasks that need real-time data access.
- Long-running agents keep context across sessions. They suit account work, case management, and ongoing research.
- Self-evolving agents improve from feedback, tests, or new rules. They need strong review because change can add new risks.
- Multi-agent systems split work among several focused agents. One may plan while another checks facts or writes a result.
Long-running agents need careful memory design. They must know what to keep, when to forget, and who may view it. Self-evolving agents need fixed tests before each update.
How to Build Autonomous AI Agents
To learn how to build autonomous AI agents, start with one narrow task. Avoid a broad goal such as “run marketing.” Choose a testable result, such as “draft a weekly campaign report.”
- Define the goal. Set the input, desired output, limits, and success measure. Include a clear stop rule.
- Map the workflow. List the steps a skilled worker takes today. Mark which steps need judgment and which need a tool.
- Pick the model and framework. Choose a model for quality, speed, cost, and context needs. Use a framework that supports tools, memory, tracing, and tests.
- Add safe tools. Give each tool one clear purpose. Validate inputs and return small, structured results.
- Build the agent loop. Let the agent read state, plan one step, call a tool, and check the result. Stop after a set number of steps.
- Add memory with care. Store only useful facts. Set access rules, retention limits, and a way to remove data.
- Test failure paths. Try missing data, bad tool output, prompt attacks, and service outages. Log each step for review.
- Release in stages. Start with read-only work. Add write actions after the agent passes set tests and human review.
Framework choice matters, but the design matters more. Your stack may include a model API, a task queue, a data store, and a tracing tool. Keep these parts replaceable when possible.
Security and privacy controls should shape the build from day one. The NIST AI Risk Management Framework offers a trusted base for risk review. Use it to link system goals with tests, owners, and controls.
Where Businesses Use Autonomous Agents
Autonomous agents in AI are useful when work has many steps and clear business rules. They can work beside staff rather than replace every task. The best first use cases have low risk and easy review.
- Marketing: Gather campaign data, spot weak channels, and draft test plans.
- Customer service: Find account details, check policy, draft replies, and route hard cases.
- Data analysis: Pull data, clean fields, run approved queries, and explain changes.
- Sales operations: Score leads, update records, and prepare meeting briefs.
- Finance: Match records, flag odd payments, and prepare review packs.
- IT support: Check logs, group alerts, and suggest safe fixes.
Consider a data analysis agent for a weekly sales report. It can fetch approved data, check missing fields, compare trends, and write a draft. A person still reviews the final numbers before release.
Measure more than task completion. Track accuracy, time saved, tool errors, cost per task, and human override rates. A fast agent that makes costly mistakes is not a useful agent.
Challenges, Security, and Human Control
Agents can fail in ways that fixed scripts do not. They may pick a poor plan, trust false data, or repeat a failed action. They may also expose private data through a tool or stored memory.
Prompt injection is one key risk. This happens when untrusted content tries to change the agent's instructions. Treat web pages, emails, files, and user text as data. Do not let them set system rules.
Use least-privilege access for every tool. Give read access before write access. Keep secrets outside the model context. Log tool calls, results, approvals, and errors.
Human review should guard high-impact actions. These include refunds, legal messages, account changes, hiring decisions, and external publishing. Set a spend limit and a time limit for each run.
Privacy also needs a clear plan. Tell users what data the agent stores and why. Set retention rules and deletion paths. Review vendors, model training terms, and data transfer routes before launch.
Finally, plan for shutdown. An operator should be able to pause runs, revoke tools, and inspect recent actions. Safe autonomy means the system can act alone within boundaries. It does not mean the system acts without oversight.
Step-by-step
- 01 Define one narrow goal
Set the input, desired result, limits, success measure, and stop rule.
- 02 Map the workflow
List each human step and mark where the agent needs judgment, data, or a tool.
- 03 Choose the model and framework
Compare quality, speed, cost, context size, tool support, tracing, and test features.
- 04 Add safe tools
Give each tool one purpose. Validate inputs and return small structured results.
- 05 Build and test the agent loop
Let the agent plan, act, check, and stop within set limits. Test bad data, tool failure, and prompt attacks.
- 06 Release in stages
Begin with read-only work. Add write actions after tests, logs, and human review pass.
Frequently asked questions
- What are autonomous AI agents?
- Autonomous AI agents are systems that pursue goals with limited human input. They can plan steps, use tools, check results, and adapt when conditions change.
- What is an autonomous AI agent used for?
- Businesses use agents for support, marketing, data analysis, sales operations, finance, and IT work. They suit tasks with many steps and clear review rules.
- How do autonomous agents differ from automation?
- Automation follows a fixed path. An autonomous agent chooses actions based on a goal, current data, and tool results.
- How do you build autonomous AI agents?
- Define one narrow goal, map the workflow, choose a model and framework, add safe tools, build the task loop, and test failure paths. Add write actions only after review.
- Are autonomous AI agents safe?
- They can be safe within strict limits, but they can still make errors or expose data. Use least-privilege access, logs, approval gates, and clear shutdown controls.
- What are long-running AI agents?
- Long-running agents keep useful context across sessions. They need memory rules for access, retention, accuracy, and deletion.
Related reading
Use AI in Real Estate to Work Smarter
See how AI can save time, find leads, and improve client service.
Learn AI and Machine Learning — Build Skills That Last
Build your AI skills with a simple path from Python to real projects.
Build AI Agents from Scratch (Beginner Path)
Build your first AI agent with simple tools, clear steps, and beginner-friendly tips.